UNYIELDING
DIGITAL PRIVACY
Pure, zero-trust WireGuard® networking engineered by Nadicorp Ltd. Zero proprietary bloatware. Compatible with official WireGuard apps across all devices, phones, and routers.
.conf & QR code generationPure, zero-trust WireGuard® networking engineered by Nadicorp Ltd. Zero proprietary bloatware. Compatible with official WireGuard apps across all devices, phones, and routers.
.conf & QR code generationNADI VPN eliminates legacy VPN protocol bloat, delivering state-of-the-art cryptography and kernel-level throughput.
Engineered directly on WireGuard for sub-millisecond handshake latency, high throughput, and minimal CPU/battery overhead across mobile and desktop devices.
Modern AEAD stream encryption paired with Curve25519 ECDH key exchange. Immune to cache-timing side-channel attacks by mathematical design.
No traffic inspection, no DNS query logging, no connection timestamps, and no user activity tracking. Sovereign privacy guaranteed by protocol design.
Enforce complete leak protection utilizing native WireGuard® client kill-switch rules and system firewall controls across Android, Windows, macOS, and Linux.
Zero passwords stored in databases. Authenticate securely with one-time cryptographic email OTPs and ephemeral device session tokens.
Engineered by Nadicorp systems researchers focusing on clean, auditable, low-overhead networking primitives without legacy protocol bloat.
No recurring subscriptions or auto-billing. Pay only for the duration you need via cryptocurrency.
Direct European relays running pure WireGuard® in Linux kernel space with zero traffic logging and low latency.
Low-Fee Cryptocurrency Settlement
Direct payments via USDT (TRC-20), LTC, SOL, TRX, DOGE, TON, XRP, BTC, and ETH. No credit cards, bank accounts, or billing addresses required.
No proprietary app bloat, no subscription locks. Pure WireGuard® configs on demand.
Select your preferred European relay node and choose a 1, 7, 15, or 30-day access pass.
Pay with USDT, LTC, SOL, TRX, or other supported coins. No credit cards or identity documents required, with automated provisioning.
Generate your Curve25519 keypair in browser, download your .conf file or scan the QR code using the official WireGuard app on any device.
See why NADI VPN chose a sovereign, kernel-native WireGuard architecture. Up to 4x faster throughput, instant handshakes, and a 96% smaller attack surface than OpenVPN or IPsec.
Instant kernel handshake
Multi-stage TLS negotiation
Formally verifiable core
Bloated legacy C codebases
Zero polling in sleep state
Continuous keepalive wakeups
WireGuard® (Kernel-Native)
Runs directly inside the Linux kernel network stack with zero user-space context switches.
OpenVPN / IPsec (User-Space)
Forces packet traversal between kernel and user-space via TUN/TAP drivers, creating memory bottlenecks.
ChaCha20-Poly1305 (AEAD)
State-of-the-art 256-bit authenticated encryption designed for high speed without hardware AES-NI chips.
AES-CBC / AES-GCM / RSA
Complex cipher suites vulnerable to downgrade attacks and padding oracle exploits.
Curve25519 (ECDH 1-RTT)
Instant cryptographic handshake with static public keys and ephemeral Noise Protocol keys.
Diffie-Hellman / RSA 2048-4096
Sluggish multi-round-trip certificate verification and large RSA key exchanges.
~4,000 Lines of C
Small enough for a single security researcher to thoroughly audit in a few days.
100,000+ Lines (OpenVPN + OpenSSL)
Enormous attack surface with dozens of historical CVE vulnerabilities and buffer overflows.
< 100ms (Immediate)
Connection established in milliseconds. No noticeable lag when switching on or waking up.
3,000ms - 8,000ms (Sluggish)
Lengthy TLS negotiations delay packet routing whenever connectivity resumes.
Seamless Handover
Cryptographic binding to client public key allows roaming across IP addresses without dropping the tunnel.
Tunnel Drop & Full Reconnect
Session drops whenever IP changes; requires complete renegotiation of TLS keys.
Silent to Unauthorized Packets
Relay nodes do not respond to unauthenticated packets, making NADI VPN ports completely invisible to port scanners.
Easily Fingerprinted & Scanned
Responds openly to handshake probing and TLS client hellos, making it trivial for ISPs to detect and throttle.
Official Open-Source WireGuard®
Zero proprietary apps required. Connect with neutral, open-source WireGuard clients on all devices.
Bloated Proprietary Clients
Forces installation of closed-source apps often bundled with diagnostic analytics and trackers.
Connect seamlessly using the official, audited WireGuard® app on all operating systems and home routers.
Official WireGuard®
Instant mobile encryption. Download official WireGuard from Play Store or App Store and scan your NADI QR code.
Official WireGuard®
One-click .conf profile import into the official WireGuard desktop client. Fast kernel-speed routing with zero bloat.
Kernel WireGuard
Native Linux WireGuard integration via wg-quick or NetworkManager with automatic DNS locking.
OpenWrt / pfSense
Protect your entire local household network with full OpenWrt, GL.iNet, pfSense, and OPNsense compatibility.

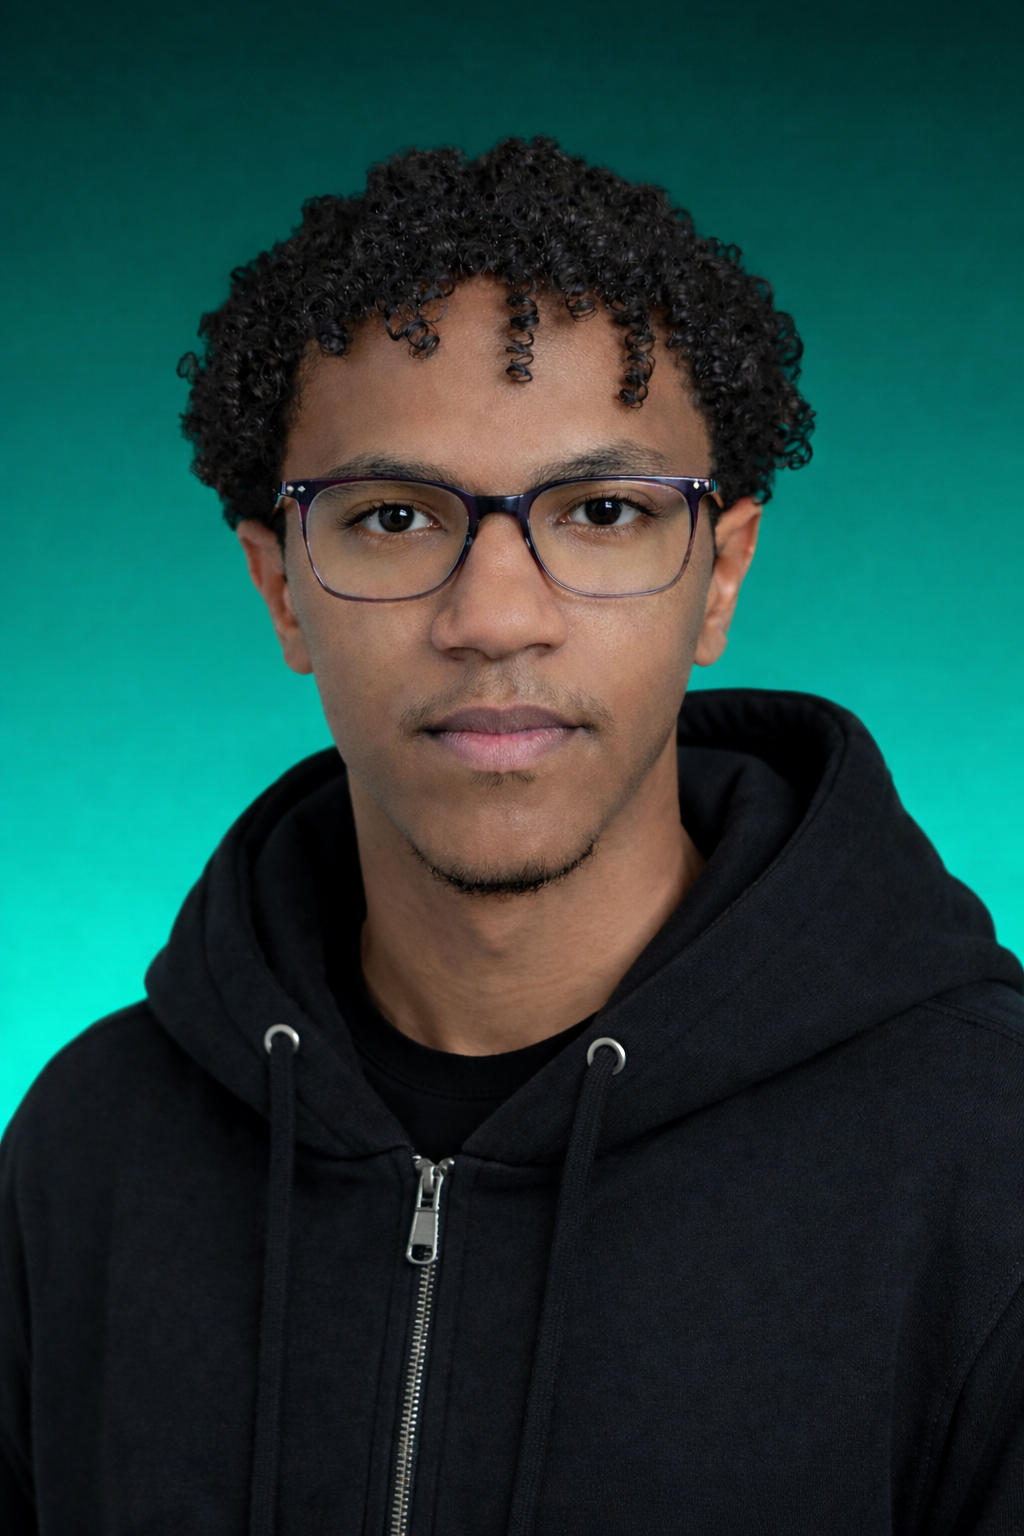
Founder & Security Researcher
NADI VPN is not a generic white-label repackage. It is an engineered zero-trust network developed under Nadicorp Ltd, a UK technology venture studio pioneering autonomous fuzzing platforms, low-level security tools, and privacy infrastructure.
Founded by Moroccan vulnerability researcher Yahya Toubali, our engineering principles prioritize mathematically provable zero-trust cryptography, audited kernel interactions, and a strict no-traffic-logs architecture.
Quick technical answers about NADI VPN, encryption, and zero-trust WireGuard passes.
WireGuard is the fastest, leanest modern VPN protocol with only ~4,000 lines of code. ChaCha20-Poly1305 is an authenticated stream cipher designed for high speeds on all CPUs (saving phone battery) and immune to cache-timing attacks.
No. NADI VPN connects strictly using the standard, official Linux kernel WireGuard® protocol on UDP port 51820. We do not provide proprietary packet obfuscation or DPI bypass layers. If an ISP or national firewall utilizes Deep Packet Inspection (DPI) to block standard WireGuard handshakes, connections may be filtered. We prioritize protocol purity, open-source auditability, and cryptographic integrity over unverified circumvention claims.
NADI VPN offers flexible zero-trust duration passes starting from $0.99 for 24 hours up to 30 days. Payments settle directly via cryptocurrency (USDT, LTC, SOL, TRX, DOGE, TON, XRP, BTC, and ETH) with no credit cards, no billing addresses, and automated provisioning upon network confirmation.
Yes. P2P and BitTorrent traffic is 100% permitted, unthrottled, and protected by our strict no-traffic-logs policy across our European relays.
No. NADI VPN maintains a strict no-traffic-logs policy. We do not inspect, log, or store browsing history, DNS queries, destination IPs, or traffic payloads. Retained operational data is strictly limited to account email (for passwordless OTP access), client WireGuard public key, and active pass expiration timestamp while your pass is active.
NADI VPN works seamlessly with official WireGuard® apps across Android, iOS/iPadOS, Windows, macOS, Linux (wg-quick), and routers (OpenWrt, pfSense). You generate your private profile or scan the QR code directly from the dashboard.
No proprietary app bloat or recurring credit card subscriptions. Generate your in-browser Curve25519 keypair and route through sovereign 10Gbps relays in 30 seconds.
1d, 7d, 15d, or 30d. From $0.99 with crypto.
Client-side Curve25519 key generated in-browser.
Import into official WireGuard®. 10Gbps unmetered.